An Ethereum savings vault operated by K3 Capital lost approximately $3.42 million in a security exploit on Wednesday, with blockchain analysis showing that block builders received $1.78 million in payments from bots competing to execute the attack. The sBOLD vault was emptied through 97 transactions in roughly eight minutes. The incident highlights how automated trading bots and transaction-ordering competition can amplify losses during decentralized finance (DeFi) exploits, allowing third parties to capture substantial value from vulnerable protocols.
sBOLD vault loses $3.42 million
The attack targeted sBOLD, a savings product developed by K3 Capital that allows users to deposit BOLD, a dollar-pegged stablecoin associated with Liquity, and earn yield through its Stability Pools.
According to Bitquery’s blockchain investigation, six wallets executed 97 transactions between approximately 12:25 and 12:33 UTC on November 18, draining the vault’s entire balance.
The exploit manipulated the vault’s share-price accounting. Attackers deposited BOLD, introduced wrapped Ether (WETH) that was initially excluded from the valuation, and subsequently converted the WETH into BOLD recognized by the vault’s accounting system. This inflated the value of their shares, allowing them to withdraw more assets than they had deposited.
The sequence was repeated several times within transactions, enabling the attackers to extract funds belonging to other depositors.
The vulnerability raised concerns about smart-contract accounting and the risks associated with automated yield-generating products. K3 Capital reportedly paused the affected vault while investigating the incident.
MEV bots and builders capture proceeds
Blockchain data show that a copycat trading bot extracted approximately $1.91 million, representing 56% of the stolen funds. The bot competed with other transactions to execute the exploit before the vault was emptied.
The competition generated substantial payments to Ethereum block builders, companies that select and arrange transactions into blocks. The payments are associated with maximal extractable value (MEV), a mechanism through which traders profit from transaction ordering.
The investigation identified Titan as the primary block builder involved, alongside BuilderNet, Ultrasound and Quasar.
Key findings from the transaction analysis include:
- Total stolen: Approximately $3.42 million.
- Builder payments: Approximately $1.78 million.
- Copycat bot extraction: Approximately $1.91 million.
- Attack duration: Roughly eight minutes.
- Transactions analyzed: 97 across six wallets.
The payments to builders reached as high as 44 ETH in a single block, demonstrating the intense competition among bots seeking transaction priority.
Security concerns and audit questions
The incident raises questions about the effectiveness of smart-contract audits and the implementation of security fixes. ChainSecurity audited sBOLD in May 2025, identifying potential value-extraction vulnerabilities associated with the vault’s accounting mechanisms.
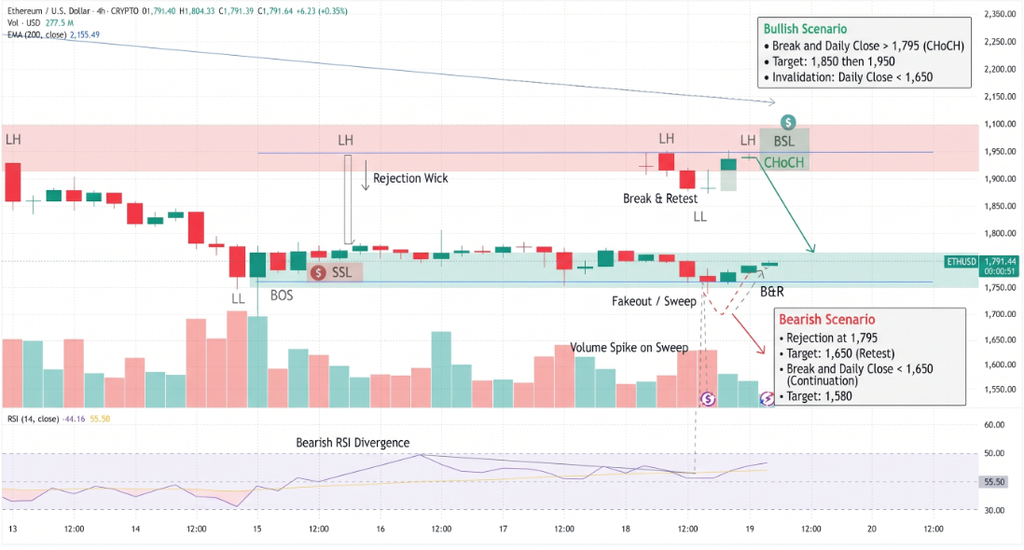
The audit stated that certain issues had been addressed in a subsequent version of the code. However, it remains unclear whether Wednesday’s exploit involved the previously identified weakness or a different accounting vulnerability.
The investigation also found that the original attacker and a wallet it funded retained approximately $520,000, considerably less than the amount received by block builders.
Conclusion
The sBOLD exploit demonstrates how vulnerable DeFi protocols can lose substantial funds within minutes, while transaction-ordering competition redirects much of the extracted value toward automated bots and block builders. The incident reinforces the importance of rigorous smart-contract audits, transparent accounting and continuous security monitoring across decentralized financial platforms.
Sources & Methodology
Primary-source standard: Market-moving facts should link to original data releases, regulator notices, company filings or official project announcements whenever available. Secondary reporting is used for additional context, not as a substitute for original evidence.
Page last reviewed: